Thursday, March 15, 2012

Proper PKI Configuration for SSL/TLS Servers

Don’t Teach Bad Habits

 A large number of servers and applications are built with SSL configured incorrectly.  If your SSL is misconfigured, it is as good as no SSL.  In reality, it may be worse than no SSL, as it gives the feeling of safety where none exists.  This is most common when developers and administrators leverage a framework that they don’t fully understand. 

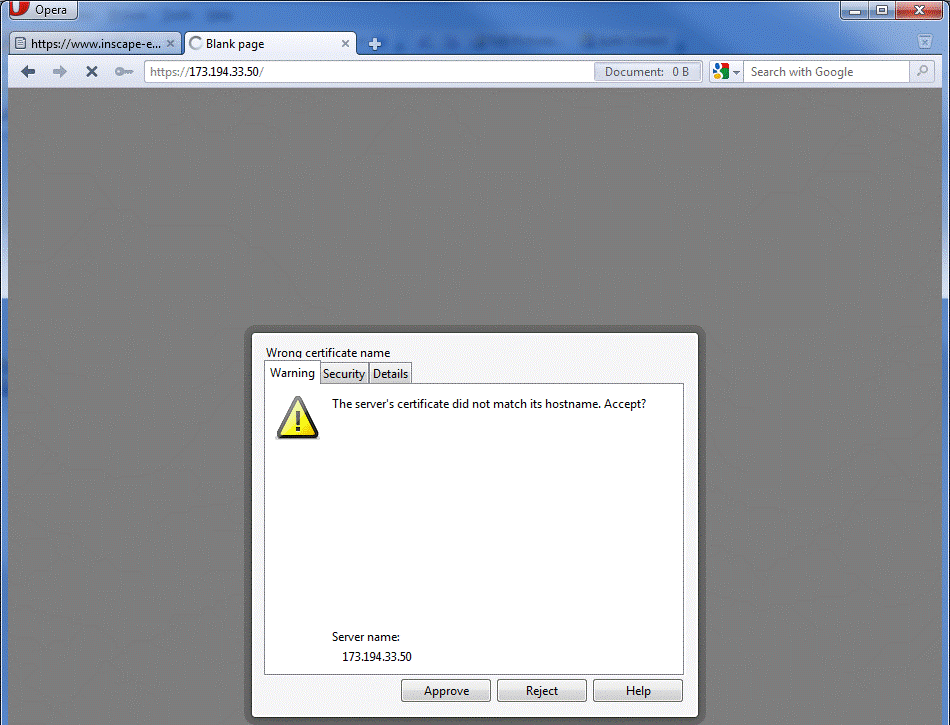
Any time a user sees one of the following errors or warnings, the server admin has failed.  A user, no matter how technical, should NEVER be forced to answer these questions.  Every time a user is trained to hit Yes, or OK to one of these errors, the user is being trained to fail.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjReRrTzqmwVJFFWLSb1SYAzSp8mKzlUd1q9k603ttHSvi0YNb3hBvgiGy7zTqPoJ9WCgxKgEfPO6fEmVISLxw44-iyPsIEKSdIWua8qWTxG9S9VtW9lPdp6ROfmY2Q2Pl8lo0BUMhCpGg/s640/1.gif

Figure 1 IE SSL Error


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjNElOXZbCZQ-DUbxZ9HSgV3nrgOiPAMlF8yRf0oRAND2TiO_N1iLFkdrnDjrO1zHehTTZTiU257xNp6sMqEuX7iUlIA4ho_C2TquB9bxE-YSFzO56WcYtb-K0aany-u8xaC_mhAYkpvg4/s640/2.gif

Figure 2 Firefox SSL Error


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEjAasqUEsIoXYXzq4ST4wSFmgbfPvk-iqmJ_sBx4PysHOZODy_60d2c4sLt6TPY5hJdrYEyFytuNI1T9UkugvRvnXOgKDMPXgh0xLKIArW2Qv1HjIYeUImpVQ2erirhBJi2mG4IxIpXgxk/s640/3.gif

Figure 3 Opera SSL Error


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEg4HkknWpgZ4PVNkU30seR_p-Duatx2AcWcAJgkv7nDqFsvMe9BdoeQiDXDgyxAnlgcH7ADXtKTJc8X9Ar6EUTub4lwSi3O5LF50ljZQxYQjaAfvNl52OgjDvq9XrWbA4s_Vn1NNozBA68/s640/4.gif

Figure 4 Chrome SSL Error


Different browsers may have slightly different text for different failures, but most users will think of them as the same thing, “The place where I have to do an extra click to get to my site”.   


Who is Protecting Whom

This document only covers standard, run of the mill SSL, where the server has a certificate and the client does not.  Two way or Mutual TLS is not commonly used and not covered here.  One of the things that confuses people about SSL is that it is designed to allow the client to protect itself and provides on protection or authentication of the client for the benefit of the server.   The server operator or application owner is supposed to be giving the client everything it needs to make sure the connection is secure.  Presumably the user is going to submit some data that he or she does not want disclosed.  If you are running an application where the liability is not on the client, standard one way SSL is not enough for you.  You are assuming a risk that you have no control over and you need additional controls.  This is the case with most online banking in the US.   If the customer loses his password to an attacker, and the attacker drains the account, in many cases, the bank is liable.  There have been a few cases recently where banks have been able to successfully put the burden on the customer.

It is safe to assume that if your application is misconfigured such that the client cannot accurately verify that the connection is secure, your end user will be able to make a successful case as to why the risk should be shifted to you, despite any Terms of Service or other contract that may state otherwise. 


Help Them Help Themselves

There are many criteria that the client can use to determine if it should trust a connection to a server.  While some clients may chose to ignore some of the criteria, it is wise to do everything right, and avoid any issues.

Subject Common Name

The Subject of the certificate is a description of the entity that offers it to a client.  To those familiar with LDAP, it may look like and x.500 Distinguished Name (DN), and it is in fact referred to as a DN.  For example:

subject=/C=US/ST=California/L=Mountain View/O=Google Inc/CN=www.google.com

However, most of the DN is arbitrary and with the inclusion of E=, for email address, it has no hierarchical convention like an LDAP DN.   While some lament this inclusion, unless there really is an LDAP to look at, who cares if the data is actually hierarchical… 

There are two exceptions to the “arbitrary” nature of the subject.  First, parties may choose to check the subject for a specific value.  Cisco VPN concentrators, for instance, can check that a certain OU or L is included.

By far the most important, for SSL/TLS is the CN, or common name.  Most clients check to make sure that the CN matches the name that the client is attempting to connect to.   This may be the most common configuration error.  The reason for this is that as a web developer, you can’t control what the user enters in their address bar.  Maybe the user will type google.com or maybe they will type www.google.com, or they might try and access some named service like maps.google.com.   They may even type in an IP address.  Often two or more of the sites may be hosted on the same server at the same IP address.  To keep things nice and consistent, many web developers may redirect the connection to the pretty named site.  This is how google does it if you enter http://google.com into the address bar:

HTTP/1.1 301 Moved Permanently

Location: http://www.google.com/


While this works great with non-SSL sites, this will fail with HTTPS unless you plan correctly.  The reason that this fails is that the SSL negotiation happens BEFORE HTTP data can be passed.  You can’t have an HTTP redirect if the SSL negotiation fails.  This is the reason that many think that you cannot use host header based virtual sites with SSL.  They are wrong, you just have to know what you are doing and get the right certificate.

We have two different options, if we want a certificate to work with multiple names.


Wild Cards Certificates

One answer to the problem of name matching is to just get one certificate that can answer for all hosts in your domain.  RFC 5425 defines a wildcard that can match any host in a domain, so the subject common name *.google.com would work for www.google.com, google.com, and mail.google.com.  While some clients seem to allow the wildcard to match domains as well as hosts, the RFC forbids this, so avoid it.  For example, *.google.com should not work for www2.maps.google.com, as only the leftmost name is the host portion.  Everything to the right is domain, and the * is not supposed to figure into domain matching.  The domain here is maps.google.com.


Subject Alternate Name

The other option, especially if you are using host headers for sites that do not share the same domain name, is to use the subject alternate name or SAN.  The SAN is a list of names that can also be checked by a client.  One certificate could then be used for www.google.com and www.gmail.com.   While clients are supposed to be able to parse both the subject common name and the SAN list, some do this poorly, therefore it is wise to add the subject common name to the list of SANs as well.


Picking the Right Name

As stated above, the client will match the name it thinks it is connecting to to the names on the certificate.  In the case of a web browser, this is the name in the address or URL bar.  This means that if your site is behind a load balance, then the common name must match the DNS name that resolves to the load balancer.  The client has no idea there may be a cluster and load balancer.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgSLXZhn_FsMMOuU30BubV2moCOBdGjA_3epWVWbF_CFsp-YsvmsfGDHfVzekSvHz31B1nL90QEd5SMoghkSF_4b6Kab_WJyAhF2G7a6IR86eS6XCJPgtLFfCkZhkBJyB0tyAGryMAqyTk/s320/5.gif


Figure 5 Typical Web Cluster


In Figure 5, the proper common name for the certificate would be www.google.com.

In some corporate environments, users may bypass the load balancer in certain circumstances.  In this case, the certificate may need SANs or to use a wild card.


Time Validity

Certificates contain a Valid From and Valid To date.  The client will check to verify that the date of the connection attempt is between the two dates.  Don’t let your certificates expire.


Certificate Revocation List Distribution Points

Generally it is thought that only PKI operators need to be concerned with CRLs and CDPs (CRL Distribution Points).  This is not the case.  A CRL is a list of certificates that the issuing CA has determined are not to be trusted.  Not all certificates list a CRL, obviously if one does not exist, you don’t care about them.  If the client determines that the certificate it is inspecting is listed on the CRL, it should reject the connection.  The reason you should be concerned with CDPs, as an application owner, is that your clients will attempt to read them.  Different clients react differently when they fail to access the CRL.  Some clients will fail open and allow the connection and some will deny it.  If you know your clients are behind highly restrictive firewalls, you may need to make sure that they have access not just to your site, but also to the CDP.  This is a common place to fail in a B2B or corporate environment.


Basic Constraints, Key Usage, and Enhanced Key Usage

A good PKI book or web site would never lump these all together, but this is neither of those.  Each of these is a field that can describe how the certificate or the associated private key can be used.  Some clients may choose to make decisions based on these.  IE for instance will allow and SSL connection to a server with no EKUs listed, but if the EKU section is used and the server authentication usages is not listed, it will deny the connection.

If the Basic Constrains listed in the certificate of the CA that signed your SSL certificate doesn’t list it as a CA, the client should abort the connection.  This keeps someone from using a certificate and private key as if it were a CA.  In the past, vendors forgot to check this, and anyone who bought a legitimate SSL certificate could use it to sign other certificates that were otherwise cryptographically sound.

Key Usage should list Digital Signature and Key Encipherment; if Key Usage is defined without Key Encipherment the client should abort the connection.  If Key Usage is not listed, all uses are allowed.


The Chain

The server’s SSL certificate does not exist in a vacuum.  It is at the bottom of a PKI hierarchy.  Without the context of the PKI the SSL certificate is useless.  The beauty of using PKI to secure (authenticate, negotiate keys and provide integrity checks) an SSL connection is that this can be done with a relatively small number of trusted third parties.  One of the big reasons to leverage PKI is to avoid the risks and overhead of increasing the number of parties you, or your clients, have to trust. 

A quick reminder about key management; there is NO WAY to exchange key material securely, over an un-trusted network, without an out of band trust being established.  Diffie–Hellman does not provide authentication, so there is no way to know which party you are negotiating with.  RSA key pairs are useless as well, as the public key must be distributed securely in order for it to be trusted.  This is why OSs, Java, web browsers, and such have keystores as part of their distributions.  Ponder this; did the browser or java package you downloaded come over via SSL or could an attacker have poisoned the keystore in the package?

The root CA is the most important element in a PKI.  The trust it conveys is significant and makes it easy to extend trust to a huge number of parties.  In order to extend this trust, subordinate CAs can propagate that trust.  It is common for a well built PKI to be two or three tiers.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiCi-xe7VRSi-vx9yrZ3B5VNaLnoxdq-NI4dHubs3hLJR-vXCDx_5fbWzbqJWFzVswLIcryKeT0QJzoucXy6UXJY_ixvoNyxsi6muSUkEu3o3W74aYa3zjhwFjDkXGjfLpwiNaxEdWW35U/s640/6.gif

Figure 6 Typical 3 Tier PKI


To increase security and usability, one should never ask a client to trust a subordinate CA or SSL certificate explicitly.  Trust should always extend implicitly from the Root CA.   Any time you ask an end user to make the decision to trust a certificate, YOU HAVE FAILED.

It’s alright to configure dev and test wrong, right? NO!!  None of your testing is valid if you don’t configure your dev and test correctly.  Additionally, dev and test are your chance to make sure you fully understand how to configure your systems correctly.  In the parlance of sports, “You play how you practice”.  So don’t practice failing.   It is well worth the extra 10 minutes to get this right.

This hierarchy is built so that a security failure at a lower level can be eliminated by simply revoking a certificate and effectively pruning an entire branch of the PKI.  Figure 6 shows the chain belonging to webmail.T-Mobile.com, whereas Figure 7 shows the entire PKI.  If the A1 CA, in Figure 7, were compromised, the root could simply revoke the A1’s certificate and A1 and everything below it would no longer be trusted.  This has no negative effect on L1C or L1B or anything below them. 


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEh-tH0yXw6yRnrQe28LnESEwbtuppdgPwJoI3beMubUGLCb7cQfFC0EtJOBtUyFZSTmeUMC1rDpwjjwQ_lhg5jPtoH-ZbA60mDtu1QSxGJ4gvx5K2n17M0UZP0x1ahD6bhZVs_kBqmpYH0/s640/7.gif

Figure 7 Big PKI


This type of design reduces the overall damage that can be done by a successful attacker.  Usually the root is offline in a vault, so it can’t be hacked.

If the client only trusts the Root, but the SSL certificate is signed by an issuing CA, like L1C in Figure 7, how does the client bridge the gap and get the trust extended to it?  The chain MUST be sent by the server as part of the SSL negotiation. 

This is another area of common misconfiguration.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgRQ_ps2dqcCrpPoqQ-3XdX-0oWveq4qRc4pIqLu0Owq08nxt6jKxR6mjHNd24dgVBPhxrApZKwBftHPcFrV2I0DlCRLKS39EgeMrESkS5Ftv5IN1QI-2RsCibDc01Uup45BhWAbYTS4EY/s640/8.gif

Figure 8 Wireshark sees 3 certificates


We see in Figure 8, a properly configured server sending the SSL certificate, the Issuer CA certificate, and the intermediate CA certificate.   If we look at the Intermediate CA certificate, it will list its issuer as the Root, Entrust, which the clients hopefully trust.  This is enough data for the client to “build” the chain and cryptographically verify that no monkey business has occurred.

As part of building the chain, the client will perform all the checks above, time validity, not revoked, etc, on each certificate in the chain.  If any check fails, the client should abort the connection.  If the chain successfully builds to the root, then the client can allow the session and security is assured.  


Forcing SSL

Another common mistake is not forcing SSL and simply enabling it.  Some site owners and designers wrongly assume that the only time they need SSL is during authentication.  If the user’s authenticated session has any value at all, then the entire session must be SSL protected.  HTTP sessions are trivial for an attacker to hijack.  Additionally, configurations on a site that mix HTTP and HTTPS are prone to human error induced problems.   Rather than trusting that links include HTTPS or that only certain pages are set to require SSL, instead set the entire site to require SSL.   All the arguments about the extra processor load of SSL haven’t been relevant since 2003 or so. 


Why All the Failures?

It would be nice if there was an easy to identify, universally hated, body like congress that could be blamed for SSL failures.  Vendors meet this requirement well.  SSL certificate vendors point their fingers at the application and OS vendors and the application and OS vendors blame the SSL certificate vendors and the open source community.  The overall problem is that there is a knowledge gap between the vendors and the admins who setup the servers and applications.  Very few admins know what the chain is, how to send it, or how to verify that it is being sent.


Verifying the Chain is Sent

Getting the chain sent, in the first place varies by application and platform, so it is best covered later.  Checking that the chain is sent is easy.  Simply install openSSL and run this command:

openssl s_client -connect host:port


This returns a very handy output full of useful information, including:

Certificate chain

 0 s:/C=US/ST=Texas/L=Frisco/O=T-Mobile USA, Inc./OU=USA/CN=webmail.T-Mobile.com

   i:/C=US/O=Entrust, Inc./OU=www.entrust.net/rpa is incorporated by reference/OU=(c) 2009 Entrust, Inc./CN=Entrust Certification Authority - L1C

 1 s:/C=US/O=Entrust, Inc./OU=www.entrust.net/rpa is incorporated by reference/OU=(c) 2009 Entrust, Inc./CN=Entrust Certification Authority - L1C

   i:/O=Entrust.net/OU=www.entrust.net/CPS_2048 incorp. by ref. (limits liab.)/OU=(c) 1999 Entrust.net Limited/CN=Entrust.net Certification Authority (2048)

 2 s:/O=Entrust.net/OU=www.entrust.net/CPS_2048 incorp. by ref. (limits liab.)/OU=(c) 1999 Entrust.net Limited/CN=Entrust.net Certification Authority (2048)

   i:/C=US/O=Entrust.net/OU=www.entrust.net/CPS incorp. by ref. (limits liab.)/OU=(c) 1999 Entrust.net Limited/CN=Entrust.net Secure Server Certification Authority

---   


0 is the SSL certificate and the numbers go up.   The subject and issuer DNs are listed to make an easy visual verification of the chain.  You can see that this application does not send the root. If you wish to verify the entire chain cryptographically, you can use the –CAfile argument and reference your Root CA certificate, in PEM format.

This would include the following line, assuming the chain checked out:

Verify return code: 0 (ok)


Sending the Chain

This section is the real reason this document was written.  There is very little guidance on the web telling admins to send the chain or how to send the chain, and often vendor documents brush over this and or don’t even cover it.

Windows

This section may be a bit of a generalization, as many applications can run on windows that use their own SSL code.  If the application uses the OS’s SSL, CAPI or CNG, then the OS will attempt to build and send chain based on what it finds in the machine store, or the store of the account running the server or application.  This will apply to all MS server applications, such as IIS, Exchange, Active Directory, etc.  Unless the developer overrides the default behaviors, this will apply to .NET apps as well.  To make sure that the OS can find the certificates in the chain, make sure that they are all in the same “My” or “Personal” store that holds the SSL certificate.  Windows can find the certificates in the other stores as well, but it is nice to know there they are and be clear which certificates are which.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgwL_GQuFJZQOtR1IL_fnbm3jUxb0Sm8V2jzaLy7PaDIqV6g0Nz6ULm48fBewbJRjMu5wmeEFqALWKumfhDWlcyTeY-kgIgL0buYjBNX6a4Iv423cGv-o47Ujlgh_yrQXCY9yWXVyIAxxE/s640/9.gif

Figure 9 Windows Machine Stores


Java

No matter which OS your JVM is running on, or the version of JVM you are running, there is one keystore that is part of the build.  The cacerts file found under lib/security holds the list of trusted CAs.  Java keystore files use passwords.  The default password for your cacerts file is ‘changeit’.  This is the list of CAs that you JVM will trust by default.  If a client side Java application will use SSL, this is the store that the trust will be based on, unless the developer made a decision to use a separate store.  The Java keystore format is proprietary, and is sometimes referred to as JKS.  Sun provides the executable ‘keytool’ to create, edit, and inspect keystore files.  Newer versions of keytool and Java seem to make it harder to mess up creating the keystore, but in older versions mistakes are very common and allowed by keytool.  The JKS file format is a password protected wrapper that should contain all the CA certificates in your chain.  Inside that wrapper is another password protected wrapper that holds the private key corresponding to your SSL certificate.   For best results, when creating your keystore file, import the CA certificates starting from the root and working down, installing the signed SSL certificate last. 

The process goes like this:

Italicizes text is entered by you.  Non-italics is command output.


Create the Keystore and Key Pair

From command prompt type the following to create keystore.

 keytool -genkey -alias sslcert -keysize 2048 -keyalg RSA -keystore keystore.jks


The following attributes must be specified.  Remember what the password is since it will be needed when setting up server and importing signed certificates.

Password: password

First and Last Name: (must be the FQDN of the server or the F5)

Organizational Unit: (ex. used Operations in particular example)

Organization: (ex. used Company USA.)

City or Locality: (ex. used Seattle)

State or Province: (ex. used Washington)

Two Letter Country Code: (ex. used US for United States)


Once attributes have been inputted, user is asked to verify information.

Select "y" and hit


The user is then asked for key password for < sslcert >, use same password type above and hit


Keystore has now been created.


Create the Certificate Signing Request

From the command line enter

keytool -certreq -alias sslcert -keystore keystore.jks -file ssl.req


Get the file ssl.req to the CA admin or vendor for signing.


Once the Certificate has been signed, the admin or vendor will return the certificate file.  In the example, this is certnew.cer.


Import the CA Hierarchy Certificates

Before importing the signed certificate into your keystore you will need to establish the trust by importing the CA Certificates.  Always start with the root CA and work your way down.  This example will show a three tier PKI.


keytool -import -trustcacerts -alias MYRoot -keystore keystore.jks -file "Company USA Root CA.cer"

Enter keystore password:  password

Owner: CN=Company USA Root CA

Issuer: CN=Company USA Root CA

Serial number: 311a0088059a3abe4afb6520a6f749d8

Valid from: Thu Jan 04 12:54:35 PST 2007 until: Mon Jan 04 13:00:47 PST 2027

Certificate fingerprints:

         MD5:  82:0D:0C:3C:24:09:D6:9C:84:A7:6D:C3:CA:44:F8:C0

         SHA1: 5F:62:6A:91:5D:0D:26:F6:FB:AF:76:92:8C:2A:F1:C6:CD:D2:66:0F

Trust this certificate? [no]:  yes

Certificate was added to keystore


keytool -import -trustcacerts -alias MYInt -keystore keystore.jks -file "Company USA Intermediate CA 01.cer"

Enter keystore password:  password

Certificate was added to keystore


keytool -import -trustcacerts -alias MYIssuer -keystore keystore.jks -file "Company USA Issuer CA 02.cer"

Enter keystore password:  password

Certificate was added to keystore


The alias creates a friendly name to list the CA in the keystore.  Each alias must be unique, so make up useful, but unique names.


Import the Signed Request File

The signed request file must be imported back into the original file.


keytool -import -trustcacerts -alias sslcert -keystore keystore.jks -file certnew.cer

Enter keystore password:  password

Certificate reply was installed in keystore


You now have a properly built Java keystore.


openSSL

openSSL is a fantastic tool and set of libraries that is leveraged by many applications.  OpenSSL’s native format for dealing with certificates, certificate signing request, and keys is the PEM format.  OpenSSL is the most versatile tool for dealing with certificates and keys, as it can convert to and from almost any format, except the Java keystore. 

A typical PEM formatted certificate looks like this:

-----BEGIN CERTIFICATE-----

MIIFuzCCBKOgAwIBAgIETBsbdDANBgkqhkiG9w0BAQUFADCBsTELMAkGA1UEBhMC

VVMxFjAUBgNVBAoTDUVudHJ1c3QsIEluYy4xOTA3BgNVBAsTMHd3dy5lbnRydXN0

…

FPagpeXsGSr0ipNqRy6m1T2mAO3Ok2B4hK6pBnhtf2n7oY1LB/e1rSIHTivJ9eaN

rOCwFjRf+bcELIi2manBx9zI0Qy8JES3vzXBG3xMkJ4Vv3QI93Uk4qn3jodtCPNj

DZZTUPbnHqRshXE6zSB7S6BvRbsmaYps9JF1+j5e3Q==

-----END CERTIFICATE-----


The chain file is just the individual CA certificates in one file, end to end, starting from the issuing CA, moving up to the root, like so:

-----BEGIN CERTIFICATE-----

MIIFuzCCBKOgAwIBAgIETBsbdDANBgkqhkiG9w0BAQUFADCBsTELMAkGA1UEBhMC

VVMxFjAUBgNVBAoTDUVudHJ1c3QsIEluYy4xOTA3BgNVBAsTMHd3dy5lbnRydXN0

…

rOCwFjRf+bcELIi2manBx9zI0Qy8JES3vzXBG3xMkJ4Vv3QI93Uk4qn3jodtCPNj

DZZTUPbnHqRshXE6zSB7S6BvRbsmaYps9JF1+j5e3Q==

-----END CERTIFICATE-----

-----BEGIN CERTIFICATE-----

MIIE8jCCA9qgAwIBAgIEOGPp/DANBgkqhkiG9w0BAQUFADCBtDEUMBIGA1UEChML

RW50cnVzdC5uZXQxQDA+BgNVBAsUN3d3dy5lbnRydXN0Lm5ldC9DUFNfMjA0OCBp

…

PFS+/i/qaZ0cHimbltjI/lGQ8SSmkAaz8Cmi/3gud1xFIdlEADHzvjJP9QoyDfz8

uhZ2VrLWSJLyi6Y+t6xcaeoLP2ZFuQ==

-----END CERTIFICATE-----

-----BEGIN CERTIFICATE-----

MIIEnzCCBAigAwIBAgIERp6RGjANBgkqhkiG9w0BAQUFADCBwzELMAkGA1UEBhMC

VVMxFDASBgNVBAoTC0VudHJ1c3QubmV0MTswOQYDVQQLEzJ3d3cuZW50cnVzdC5u

…

RfPB+JbFi1WkzGuDFiAy2r77r5u3n+F+hJ+ePFCnP1zCvouGuAiS7vhCKw0T43aF

SApKv9ClOwqwVLht4wj5NI0LjosSzBcaM4eVyJ4K3FBTF3s=

-----END CERTIFICATE-----


Note that the begin and end certificate statements are left in place. 

To create a key pair and certificate signing request do the following:

openssl req -new -newkey rsa:2048 -nodes -out file.csr -keyout file.key

This will output your key files and CSR.  The vendor or PKI admin should sign the CSR and return your SSL certificate as well as the CA certificate in your chain.

With the returned files and openSSL, the sky is the limit.


Apache

First off, there are a couple of ways to configure HTTPS on apache.  The main methods are via mod_ssl and Apache-SSL.  Apache-SSL has not been updated in a while and should be avoided.

Mod_ssl uses openSSL libraries, so you will need openSSL to do anything fun.  The native file format for openSSL is called PEM or base64, which are text files, rather than the DER format, that is binary. 

The file that will contain your SSL settings is the httpd.conf file.  There are three settings that you will care about.

SSLCertificateFile  -  This is the actual SSL certificate

SSLCertificateKeyFile  -  this is the associated private key file.  If there is a pass phrase on the key, it must be entered at startup.  This may not be appropriate for some environments.

SSLCertificateChainFile  - This is chain file as described above.

F5 Local Traffic Manager – BigIP

First of all, you probably should not be terminating SSL on your F5.  “Need to know” or “reduced surface area” says that you don’t want the F5 techs to be able to see your decrypted traffic.  There are few good cases for decrypting SSL at the F5.  If you need to inspect host headers or URLs, this may be necessary.

F5 uses openSSL so the section above will help get the needed key and cert material.

In the SSL Client Profile, there is an option to set the Chain file.  Simply copy over the chain file in the openSSL format and apply the setting.


Forcing SSL

SSL should be forced at the web site level, to eliminate human error.

IIS

In IIS you can define the SSL settings at the site level, virtual directory level, or the page/object level.  The best place to do this is at the site level.


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEiygGNG4F6YKvQzWNczNfkgXoxkrwC2faBO4PLBfvu6btCXjABgDpgOugO2dpA4YggOgsSKcNDQA9K_3uYWCMgcPnlBNUGpKCCkrQIxnHS4audY4Yas_bdRyhyphenhyphenU8jVmiOxqrYy8hHNYXU0/s640/10.gif

Figure 10 Requiring SSL in IIS6


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhO5xaxGZruhYzmCFx9pjkyKumgGjVlyYIQOKWDZVYQGNRSnMWwWLi-YG2fsHpdJpsUP2VIt1OoPyKHDlJVazvqYXTNTfQ0GDPiUM892bW-jp7jpWJbFKUrMHuKAtflTZ2T2BCMpPc9q6g/s640/11.gif

Figure 11 Requiring SSL in IIS7


In order to make a better experience, consider changing the default 403.4 HTTP error page to a redirect page, so the user does not get an ugly error.


Apache

In the httpd.conf file, use the directive SSLRequireSSL to require SSL all the time.  http://httpd.apache.org/docs/2.0/mod/mod_ssl.html#sslrequiressl

In order to make the end user experience better, consider implementing a redirect from HTTP to HTTPS, rather than just blocking HTTP.  http://www.besthostratings.com/articles/force-ssl-htaccess.html


F5 LTM

The LTM does not have extra ports setup by default.  If you do not setup the HTTP port, the user will get a server not found error.  Consider creating a VIP and iRule that redirects the user to your HTTPS site.

The iRule would look like this:

when HTTP_REQUEST {

HTTP::redirect "https://[HTTP::host][HTTP::uri]"

}  


This simply redirects the browser, rewriting the URL with and HTTPS replacing the HTTP.


Not Covered

A few things may seem to be missing here.  This document focuses on PKI related configuration.  Different apps and OSs also have other SSL/TLS settings that are not directly related to PKI. 


Cipher Suites

As part of the SSL negotiation, the client and server agree on a ciphersuite that is common to them both, hopefully the strongest common suite.  As attacks and computing power change, the “best” ciphers change.   It is called a suites, as it defines ciphers users in four areas, authentication, key exchange, messaged integrity check (MAC), and the bulk (symmetric) cipher used, including mode, for block ciphers.  There is a wide array of combinations of these parameters.  As the suite is only as strong as its weakest link, most ciphersuites should be eliminated from your configuration.  As of December 2011, you should eliminate any suite that sets any of the four areas to null.  You should eliminate any suite that relies on MD5 for its MAC. You should eliminate any ciphersuite that uses a block cipher in CBC mode.  One should also eliminate suites that utilize a symmetric cipher with a key shorter than 128 bit.

For more on CipherSuites, see http://tools.ietf.org/html/rfc4346


Windows

Microsoft allows you to pick the ciphersuites you will allow, as well as prioritize how they will be negotiated.  A good place to start is here http://msdn.microsoft.com/en-us/library/windows/desktop/aa374757(v=vs.85).aspx .

We aware that XP/2003 and Win7/2008 have different settings and available suites.


Java

The Java Class SSLSocket allows the developer to adjust the suites used.   http://docs.oracle.com/javase/1.4.2/docs/api/javax/net/ssl/SSLSocket.html


F5


Apache

Apache support for changing your ciphersuite can be found here http://httpd.apache.org/docs/2.0/ssl/ssl_howto.html


Mixed Content

I won't go into how to fix it, or configure your systems, cause you don't pay me...  but, creating a page that uses SSL, but that has elements in the page that are not over SSL is called creating mixed content.  This is common for those who use CDNs, as their images are all served up via HTTP.  


Mixed content gives the user fun symbols that indicate badness, but how bad??  We can't expect users to make the call on this kind of thing.  


https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEgrOnxWOUV0o3mwoyuPRq2c1Y76MCXtYkr0Rl-cOl1T1h0ZOnINLv4bvjdUlkPGH87TLFfb_1t5zR21rukObqwagO0viU6oW1K3XT6I7yYx8GPWquInURDgmEdDGTCZ_Vn7qlH90WUo0hU/s1600/12.gif

Figure 12 Google Reader Throwing Mixed Content Error in Chrome 


What's a user supposed to think when they encounter Figure 12?  Can your mom or grandfather get meaning out of this explanation?  https://support.google.com/chrome/bin/answer.py?hl=en&answer=95617 


Summary

If you want to make the customer experience good, and avoid litigation, make sure to configure SSL on your web servers correctly.  Any failure in your configuration may put the client at risk, but it may be a risk that is assumed by you, due to contracts.

Make sure you:

  • Set the right subject common name
  • Send the chain
  • Have time valid certificates
  • Include the right usage information
  • Force SSL
  • Have verified that the CRLs can be reached
  • CHECK YOUR WORK

Friday, March 2, 2012

Enrique Salem, president and CEO, Symantec, I WANT MY $2

As my readers know, in May of 2011, I coined and began protecting the terms "Advanced Persistent Protection", "Advance Persistent Controls", and "Advanced Persistent Control Suite".

This week, my brilliant reader Sterling pointed out that I now have one peer who agrees with me, Enrique Salem, president and CEO of Symantec.  In a post for SC Magazine, he makes four bullet points about Advanced Persistent Protection. I'm thinking three is the limit for reasonable use.  If Symantec is going to start pimping my copyrighted phrase, they need to pay!

I am currently in talks with Michael “Let’s Get Ready to Rumble” Buffer's legal team to get my cash out of these guys.

Symantec, I have no desire to litigate as long as you give me what I am due.  I'm glad to take a per use fee or we can negotiate an exclusive long term deal if you'd prefer.  You'd better hurry though, RSA has already started talks. I'd hate for this to sink your upcoming marketing campaign.

Cheers,

Mark

Thursday, December 15, 2011

Advanced Persistent Threats - Thank You Wikipedia

My head is near exploding, as I'm sure yours is, from all the APT news.  It's everywhere, I swear I saw it on the cover of the Weekly World News.

What annoys me is that the first several times I heard about an APT, "they" were basically describing any other virus or malware.  The only difference was that the writers did a better job hiding their command and control, and they used more, and varying, ways to hide from AV and stay resident.  This is a lame term as there is no line where quality achieves the level of Advanced!!

After hearing about the nature of the RSA breach, I have decided to only give credence to those who refer to an APT as an actor.  APTs are not code.  An APT is someone, some organization, or a nation state who is well funded, highly sophisticated, and persistent in their goal to compromise something.

I went to Wikipedia to see what the masses were saying, assuming the worst.  Wikipedia agrees with me?  I may  have to turn in my security spurs.  :-P

Proper use, "I am an advanced persistent threat".

Improper user, "I created an advanced persistent threat".

You can kill or jail an advanced persistent threat, but you can't delete it.

Tuesday, November 22, 2011

LDAP Tool of the Day - getrootDSE

I'm an LDAP guy.  I'm not even sure what that means, but I am one.  I spend a lot of my work time looking at LDAPs.  For the purists, I look at directories.  LDAP is just an interface to the directory.  If I look at the protocol with Wireshark, does that mean I am looking at LDAPs, 'cuase I do that too.  Can you really look at a directory?  I've never been to our data centers.  Where was I?

There are a lot of great tools for working with LDAP, but there is always room for one more, right?   A common task for me is to need to look at the contents of the Root DSE and verify the SSL certificate being used, if SSL is used.

For those not familiar with the root DSE, it is an entry offered by all LDAP servers.  Its DN is null or empty, depending on how you interpret the RFCs.  It almost always accepts un-authenticated connections and lists information about the contents and capabilities of the LDAP server.  It will usually list the supported LDAP controls, authentication types offered, and often the naming contexts is holds.  Different vendors list different data, and it is this data that I am often interested in.

Here are a few typical entries:
Active Directory Domain Controller 

dn:
currentTime: 20111123000138.0Z
subschemaSubentry: CN=Aggregate,CN=Schema,CN=Configuration,DC=example,DC=org
dsServiceName: CN=NTDS Settings,CN=mydomcontr08,CN=Servers,CN=Food,CN=Sites,CN=Co
 nfiguration,DC=example,DC=org
namingContexts: DC=example,DC=org
namingContexts: CN=Configuration,DC=example,DC=org
namingContexts: CN=Schema,CN=Configuration,DC=example,DC=org
defaultNamingContext: DC=example,DC=org
schemaNamingContext: CN=Schema,CN=Configuration,DC=example,DC=org
configurationNamingContext: CN=Configuration,DC=example,DC=org
rootDomainNamingContext: DC=example,DC=org
supportedControl: 1.2.840.113556.1.4.319
supportedControl: 1.2.840.113556.1.4.801
supportedControl: 1.2.840.113556.1.4.473
supportedControl: 1.2.840.113556.1.4.528
supportedControl: 1.2.840.113556.1.4.417
supportedControl: 1.2.840.113556.1.4.619
supportedControl: 1.2.840.113556.1.4.841
supportedControl: 1.2.840.113556.1.4.529
supportedControl: 1.2.840.113556.1.4.805
supportedControl: 1.2.840.113556.1.4.521
supportedControl: 1.2.840.113556.1.4.970
supportedControl: 1.2.840.113556.1.4.1338
supportedControl: 1.2.840.113556.1.4.474
supportedControl: 1.2.840.113556.1.4.1339
supportedControl: 1.2.840.113556.1.4.1340
supportedControl: 1.2.840.113556.1.4.1413
supportedControl: 2.16.840.1.113730.3.4.9
supportedControl: 2.16.840.1.113730.3.4.10
supportedControl: 1.2.840.113556.1.4.1504
supportedControl: 1.2.840.113556.1.4.1852
supportedControl: 1.2.840.113556.1.4.802
supportedControl: 1.2.840.113556.1.4.1907
supportedControl: 1.2.840.113556.1.4.1948
supportedControl: 1.2.840.113556.1.4.1974
supportedControl: 1.2.840.113556.1.4.1341
supportedControl: 1.2.840.113556.1.4.2026
supportedLDAPVersion: 3
supportedLDAPVersion: 2
supportedLDAPPolicies: MaxPoolThreads
supportedLDAPPolicies: MaxDatagramRecv
supportedLDAPPolicies: MaxReceiveBuffer
supportedLDAPPolicies: InitRecvTimeout
supportedLDAPPolicies: MaxConnections
supportedLDAPPolicies: MaxConnIdleTime
supportedLDAPPolicies: MaxPageSize
supportedLDAPPolicies: MaxQueryDuration
supportedLDAPPolicies: MaxTempTableSize
supportedLDAPPolicies: MaxResultSetSize
supportedLDAPPolicies: MaxNotificationPerConn
supportedLDAPPolicies: MaxValRange
highestCommittedUSN: 124867805
supportedSASLMechanisms: GSSAPI
supportedSASLMechanisms: GSS-SPNEGO
supportedSASLMechanisms: EXTERNAL
supportedSASLMechanisms: DIGEST-MD5
dnsHostName: mydomcontr08.example.ORG
ldapServiceName: example.ORG:mydomcontr08$@example.ORG
serverName: CN=mydomcontr08,CN=Servers,CN=Food,CN=Sites,CN=Configuration,DC=examp
 le,DC=org
supportedCapabilities: 1.2.840.113556.1.4.800
supportedCapabilities: 1.2.840.113556.1.4.1670
supportedCapabilities: 1.2.840.113556.1.4.1791
supportedCapabilities: 1.2.840.113556.1.4.1935
isSynchronized: TRUE
isGlobalCatalogReady: TRUE
domainFunctionality: 2
forestFunctionality: 2
domainControllerFunctionality: 3

Oracle Virtual Directory
dn:
namingContexts: ou=Groups,dc=example,dc=com
namingContexts: ou=admins,dc=example,dc=com
namingContexts: ou=employees,dc=example,dc=com
namingContexts: ou=IDMUsers,dc=idm.example,dc=com
namingContexts: ou=partners,dc=example,dc=com
namingContexts: OU=portal users,dc=example,dc=com
namingContexts: dc=example,dc=com
namingContexts: ou=OIDUsers,dc=idm.example,dc=com
objectClass: top
subschemaSubEntry: cn=schema
supportedSASLMechanisms: EXTERNAL
supportedSASLMechanisms: CRAM-MD5
supportedLDAPVersion: 2
supportedLDAPVersion: 3
supportedExtension: 1.3.6.1.4.1.1466.20037

Oracle Internet Directory
dn:
supportedsaslmechanisms: DIGEST-MD5
supportedldapversion: 2
supportedldapversion: 3
supportedextension: 2.16.840.1.113894.1.9.1
supportedextension: 1.3.6.1.4.1.1466.20037
supportedcontrol: 2.16.840.1.113730.3.4.2
supportedcontrol: 2.16.840.1.113894.1.8.1
supportedcontrol: 2.16.840.1.113894.1.8.2
supportedcontrol: 2.16.840.1.113894.1.8.3
supportedcontrol: 2.16.840.1.113894.1.8.4
supportedcontrol: 2.16.840.1.113894.1.8.5
supportedcontrol: 2.16.840.1.113894.1.8.6
supportedcontrol: 2.16.840.1.113894.1.8.7
supportedcontrol: 1.2.840.113556.1.4.473
supportedcontrol: 1.2.840.113556.1.4.319
supportedcontrol: 2.16.840.1.113894.1.8.14
supportedcontrol: 2.16.840.1.113894.1.8.16
supportedcontrol: 2.16.840.1.113894.1.8.23
supportedcontrol: 2.16.840.1.113894.1.8.29
subschemasubentry: cn=subschemasubentry
subregistrysubentry: cn=subregistrysubentry
subconfigsubentry: cn=subconfigsubentry
pwdpolicysubentry: cn=default,cn=pwdPolicies,cn=Common,cn=Products,cn=OracleCont
 ext
orclupgradeinprogress: FALSE
orcltimelimit: 3600
orclstatsperiodicity: 60
orclstatslevel: 0
orclstatsflag: 0
orclsizelimit: 100000
orclsimplemodchglogattributes: uniquemember
orclsimplemodchglogattributes: member
orclsimplemodchglogattributes: orcluserapplnprovstatus
orclsimplemodchglogattributes: orcluserapplnprovstatusdesc
orclsimplemodchglogattributes: orcluserprovfailurecount
orclservermode: rw
orclreplicaid: prdoidx401_poid1
orclreplagreements: cn=replication configuration
orcloptcontainsquery: 0
orclnormdn:: IA==
orclmaxtcpidleconntime: 120
orclmatchdnenabled: 0
orcllegacyoidsyncagent: cn=odisrv+orclhostname=prdoidx001,cn=Registered Instance
 s,cn=Directory Integration Platform,cn=Products,cn=OracleContext
orcllegacyoidsyncagent: cn=odisrv+orclhostname=prdoidx401,cn=Registered Instance
 s,cn=Directory Integration Platform,cn=Products,cn=OracleContext
orcllegacyoidsyncagent: cn=odisrv+orclhostname=prdoidx002,cn=Registered Instance
 s,cn=Directory Integration Platform,cn=Products,cn=OracleContext
orcllegacyoidsyncagent: cn=odisrv+orclhostname=prdoidx402,cn=Registered Instance
 s,cn=Directory Integration Platform,cn=Products,cn=OracleContext
orcleventlevel: 0
orclentrylevelaci: access to entry by * (browse, noadd, nodelete)
orclentrylevelaci: access to attr=(orclaci,orclguname,orclgupassword,orclprname,
 orclprpassword,orclcryptoscheme,orclsuname,orclsupassword) by * (none)
orclentrylevelaci: access to attr=(*) by * (search, read, nowrite, nocompare)
orclentrylevelaci: access to attr=(*) AppendToAll by group="cn=directoryadmingro
 up,cn=oracle internet directory" (search,read,write,compare)
orclentrylevelaci: access to entry AppendToAll by group="cn=directoryadmingroup,
 cn=oracle internet directory" (browse,add,delete)
orclentrylevelaci: access to attr=(orclstatsflag, orclstatsperiodicity,orclevent
 level) by dn="cn=emd admin,cn=oracle internet directory" (search,read,write,com
 pare) by * (search,read)
orclenablegroupcache: 1
orclecachemaxsize: 10000000
orclecachemaxentries: 25000
orclecacheenabled: 1
orcldirectoryversion: OID 10.1.4.3.0
orcldiprepository: FALSE
orcldebugop: 511
orcldebugflag: 0
orclcatalogentrydn: cn=catalogs
orclauditlevel: 0
orclanonymousbindsflag: 1
matchingrules: distinguishedNameMatch
matchingrules: caseIgnoreMatch
matchingrules: caseExactMatch
matchingrules: numericStringMatch
matchingrules: telephoneNumberMatch
changestatus: cn=changestatus
changelog: cn=changelog
authpassword;oid: {SASL/MD5}sHex432oGONWYembe52eKA==
authpassword;oid: {SASL/MD5-DN}UpdstrkdNdL5mxyQ8wFP5iQ==
authpassword;oid: {SASL/MD5-U}m0/awjpasdf346gaKaIHs9UQ==


One can get this all via the command line, with ldapsearch.  For windows, I use the OpenDS version.

>ldapsearch -h host.name.org  -p 389 -w "" -b "" -s base  objectclass=*

I often forget the command, and if you need SSL, then you need to add -Z -X.  Really, the -X is something that I'd complain about in most contexts, as it accepts any SSL certs.  In this case, I am meaning to investigate the cert as well.

This gets me the LDAP info, but, then I'd need to use openssl to get the SSL and cert info.

Using
>openssl s_client -connect ovd.internal.example.com:636
I get the connect info:

Loading 'screen' into random state - done
CONNECTED(0000017C)
depth=3 CN = Example USA Root CA
verify error:num=19:self signed certificate in certificate chain
verify return:0
---
Certificate chain
 0 s:/C=US/ST=Washington/L=Bothell/O=Example USA, Inc./OU=Internal Systems/CN=ovd.internal.Example.com
   i:/DC=org/DC=Example/CN=Example USA Issuer CA 02
 1 s:/DC=org/DC=Example/CN=Example USA Issuer CA 02
   i:/CN=Example USA Intermediate CA 01
 2 s:/CN=Example USA Intermediate CA 01
   i:/CN=Example USA Root CA
 3 s:/CN=Example USA Root CA
   i:/CN=Example USA Root CA
---
Server certificate
-----BEGIN CERTIFICATE-----
MIIGFTCCBP2gAwIBAgIKN3rWsgABAAWq7TANBgkqhkiG9w0BAQUFADBSMRMwEQYK
CZImiZPyLGQBGRYDb3JnMRcwFQYKCZImiZPyLGQBGRYHZ3NtMTkwMDEiMCAGA1UE
AxMZVC1Nb2JpbGUgVVNBIElzc3VlciBDQSAwMjAeFw0xMTAxMzAwMTU2MjlaFw0x
MjAxMzAwMTU2MjlaMIGQMQswCQYDVQQGEwJVUzETMBEGA1UECBMKV2FzaGluZ3Rv
.
.
hpw6x12bNa5bqIzyCm70ENEWSZkVAIiYPgNlJEs4AjmzgHo9ixPqsRmzSbmryaAg
8Pw6PUYagF+4soVfKRTZm62m+6qHlmnsDeGjKh6YR7QSwySTH+LV0VXuPBecM7T9
tf90c4mUD/jKnk9o0up0yTxXDf/WKNQ9SHKkzxvqJ8+7DcVw5kjBe+x8H1/HK420
skqyrngmSrL/3xjN/9JdXJp3WRVa+2dYAg==
-----END CERTIFICATE-----
subject=/C=US/ST=Washington/L=Bothell/O=Example USA, Inc./OU=Internal Systems/CN=ovd.internal.Example.com
issuer=/DC=org/DC=Example/CN=Example USA Issuer CA 02
---
No client certificate CA names sent
---
SSL handshake has read 6038 bytes and written 368 bytes
---
New, TLSv1/SSLv3, Cipher is EDH-RSA-DES-CBC3-SHA
Server public key is 1024 bit
Secure Renegotiation IS supported
Compression: NONE
Expansion: NONE
SSL-Session:
    Protocol  : TLSv1
    Cipher    : EDH-RSA-DES-CBC3-SHA
    Session-ID: 4ECC3B5303F3EAB7AFDD9452D7671A08CA4E345DF07F7FF3A76A3B9C62B2DA10
    Session-ID-ctx:
    Master-Key: B074BCE20BBF51B4EF420994309A4CC3DD85DB48F9CB6C5305F984A936FD6B659588C942B63FBC0228EF570D7E05777F
    Key-Arg   : None
    PSK identity: None
    PSK identity hint: None
    Start Time: 1322007377
    Timeout   : 300 (sec)
    Verify return code: 19 (self signed certificate in certificate chain)
---

Last, I have to cut and paste the certificate into a file and use openssl to read it.
>openssl asn1parse -in "cert.pem"

    0:d=0  hl=4 l=1557 cons: SEQUENCE
    4:d=1  hl=4 l=1277 cons: SEQUENCE
    8:d=2  hl=2 l=   3 cons: cont [ 0 ]
   10:d=3  hl=2 l=   1 prim: INTEGER       :02
   13:d=2  hl=2 l=  10 prim: INTEGER       :377AD6B200010005AAED
   25:d=2  hl=2 l=  13 cons: SEQUENCE
   27:d=3  hl=2 l=   9 prim: OBJECT        :sha1WithRSAEncryption
   38:d=3  hl=2 l=   0 prim: NULL
   40:d=2  hl=2 l=  82 cons: SEQUENCE
   42:d=3  hl=2 l=  19 cons: SET
   44:d=4  hl=2 l=  17 cons: SEQUENCE
   46:d=5  hl=2 l=  10 prim: OBJECT        :domainComponent
   58:d=5  hl=2 l=   3 prim: IA5STRING     :org
   63:d=3  hl=2 l=  23 cons: SET
   65:d=4  hl=2 l=  21 cons: SEQUENCE
   67:d=5  hl=2 l=  10 prim: OBJECT        :domainComponent
   79:d=5  hl=2 l=   7 prim: IA5STRING     :gsm1900
   88:d=3  hl=2 l=  34 cons: SET
   90:d=4  hl=2 l=  32 cons: SEQUENCE
   92:d=5  hl=2 l=   3 prim: OBJECT        :commonName
   97:d=5  hl=2 l=  25 prim: PRINTABLESTRING   :Example USA Issuer CA 02
  124:d=2  hl=2 l=  30 cons: SEQUENCE
  126:d=3  hl=2 l=  13 prim: UTCTIME       :110130015629Z
  141:d=3  hl=2 l=  13 prim: UTCTIME       :120130015629Z
  156:d=2  hl=3 l= 144 cons: SEQUENCE
  159:d=3  hl=2 l=  11 cons: SET
  161:d=4  hl=2 l=   9 cons: SEQUENCE
  163:d=5  hl=2 l=   3 prim: OBJECT        :countryName
  168:d=5  hl=2 l=   2 prim: PRINTABLESTRING   :US
  172:d=3  hl=2 l=  19 cons: SET
  174:d=4  hl=2 l=  17 cons: SEQUENCE
  176:d=5  hl=2 l=   3 prim: OBJECT        :stateOrProvinceName
  181:d=5  hl=2 l=  10 prim: PRINTABLESTRING   :Washington
  193:d=3  hl=2 l=  16 cons: SET
  195:d=4  hl=2 l=  14 cons: SEQUENCE
  197:d=5  hl=2 l=   3 prim: OBJECT        :localityName
  202:d=5  hl=2 l=   7 prim: PRINTABLESTRING   :Bothell
  211:d=3  hl=2 l=  27 cons: SET
  213:d=4  hl=2 l=  25 cons: SEQUENCE
  215:d=5  hl=2 l=   3 prim: OBJECT        :organizationName
  220:d=5  hl=2 l=  18 prim: PRINTABLESTRING   :Example USA, Inc.
  240:d=3  hl=2 l=  25 cons: SET
  242:d=4  hl=2 l=  23 cons: SEQUENCE
  244:d=5  hl=2 l=   3 prim: OBJECT        :organizationalUnitName
  249:d=5  hl=2 l=  16 prim: PRINTABLESTRING   :Internal Systems
  267:d=3  hl=2 l=  34 cons: SET
  269:d=4  hl=2 l=  32 cons: SEQUENCE
  271:d=5  hl=2 l=   3 prim: OBJECT        :commonName
  276:d=5  hl=2 l=  25 prim: PRINTABLESTRING   :ovd.internal.Example.com
  303:d=2  hl=3 l= 159 cons: SEQUENCE
  306:d=3  hl=2 l=  13 cons: SEQUENCE
  308:d=4  hl=2 l=   9 prim: OBJECT        :rsaEncryption
  319:d=4  hl=2 l=   0 prim: NULL
  321:d=3  hl=3 l= 141 prim: BIT STRING
  465:d=2  hl=4 l= 816 cons: cont [ 3 ]
  469:d=3  hl=4 l= 812 cons: SEQUENCE
  473:d=4  hl=2 l=  29 cons: SEQUENCE
  475:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 Subject Key Identifier
  480:d=5  hl=2 l=  22 prim: OCTET STRING      [HEX DUMP]:0414D5FBEBB564FC0855035A02C36F05D3BE6AB6D990
  504:d=4  hl=2 l=  31 cons: SEQUENCE
  506:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 Authority Key Identifier
  511:d=5  hl=2 l=  24 prim: OCTET STRING      [HEX DUMP]:30168014688A27CD6281B170FAC4A241E1F84927278B3A00
  537:d=4  hl=4 l= 305 cons: SEQUENCE
  541:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 CRL Distribution Points
  546:d=5  hl=4 l= 296 prim: OCTET STRING      [HEX DUMP]:  
  846:d=4  hl=4 l= 294 cons: SEQUENCE
  850:d=5  hl=2 l=   8 prim: OBJECT        :Authority Information Access
  860:d=5  hl=4 l= 280 prim: OCTET STRING      [HEX DUMP]:
 1144:d=4  hl=2 l=  12 cons: SEQUENCE
 1146:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 Basic Constraints
 1151:d=5  hl=2 l=   1 prim: BOOLEAN       :255
 1154:d=5  hl=2 l=   2 prim: OCTET STRING      [HEX DUMP]:3000
 1158:d=4  hl=2 l=  11 cons: SEQUENCE
 1160:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 Key Usage
 1165:d=5  hl=2 l=   4 prim: OCTET STRING      [HEX DUMP]:030205A0
 1171:d=4  hl=2 l=  62 cons: SEQUENCE
 1173:d=5  hl=2 l=   9 prim: OBJECT        :1.3.6.1.4.1.311.21.7
 1184:d=5  hl=2 l=  49 prim: OCTET STRING      [HEX DUMP]:302F06272B0601040182371508AFAB1B85DD9D4F82E999398785C52C83F1EE
23778AC8DE812D86D8DA8E14020164020106
 1235:d=4  hl=2 l=  19 cons: SEQUENCE
 1237:d=5  hl=2 l=   3 prim: OBJECT        :X509v3 Extended Key Usage
 1242:d=5  hl=2 l=  12 prim: OCTET STRING      [HEX DUMP]:300A06082B06010505070301
 1256:d=4  hl=2 l=  27 cons: SEQUENCE
 1258:d=5  hl=2 l=   9 prim: OBJECT        :1.3.6.1.4.1.311.21.10
 1269:d=5  hl=2 l=  14 prim: OCTET STRING      [HEX DUMP]:300C300A06082B06010505070301
 1285:d=1  hl=2 l=  13 cons: SEQUENCE
 1287:d=2  hl=2 l=   9 prim: OBJECT        :sha1WithRSAEncryption
 1298:d=2  hl=2 l=   0 prim: NULL
 1300:d=1  hl=4 l= 257 prim: BIT STRING


I can get 98% of what I need in one command, with my new tool


>getrootdse myORG.org 636 ssl


Performing a RootDSE search ...
supportedSASLMechanisms   is GSSAPI
supportedSASLMechanisms   is GSS-SPNEGO
supportedSASLMechanisms   is EXTERNAL
supportedSASLMechanisms   is DIGEST-MD5
defaultNamingContext   is DC=myORG,DC=org
domainControllerFunctionality   is 3
ldapServiceName   is myORG.org:myDomcontr01$@myORG.ORG
supportedLDAPVersion   is 3
supportedLDAPVersion   is 2
dsServiceName   is CN=NTDS Settings,CN=myDomcontr01,CN=Servers,CN=myORG-West,CN=Sites,CN=Configurati
on,DC=myORG,DC=org
subschemaSubentry   is CN=Aggregate,CN=Schema,CN=Configuration,DC=myORG,DC=org
supportedLDAPPolicies   is MaxPoolThreads
supportedLDAPPolicies   is MaxDatagramRecv
supportedLDAPPolicies   is MaxReceiveBuffer
supportedLDAPPolicies   is InitRecvTimeout
supportedLDAPPolicies   is MaxConnections
supportedLDAPPolicies   is MaxConnIdleTime
supportedLDAPPolicies   is MaxPageSize
supportedLDAPPolicies   is MaxQueryDuration
supportedLDAPPolicies   is MaxTempTableSize
supportedLDAPPolicies   is MaxResultSetSize
supportedLDAPPolicies   is MaxNotificationPerConn
supportedLDAPPolicies   is MaxValRange
isSynchronized   is TRUE
dnsHostName   is myDomcontr01.myORG.org
supportedControl   is 1.2.840.113556.1.4.319
supportedControl   is 1.2.840.113556.1.4.801
supportedControl   is 1.2.840.113556.1.4.473
supportedControl   is 1.2.840.113556.1.4.528
supportedControl   is 1.2.840.113556.1.4.417
supportedControl   is 1.2.840.113556.1.4.619
supportedControl   is 1.2.840.113556.1.4.841
supportedControl   is 1.2.840.113556.1.4.529
supportedControl   is 1.2.840.113556.1.4.805
supportedControl   is 1.2.840.113556.1.4.521
supportedControl   is 1.2.840.113556.1.4.970
supportedControl   is 1.2.840.113556.1.4.1338
supportedControl   is 1.2.840.113556.1.4.474
supportedControl   is 1.2.840.113556.1.4.1339
supportedControl   is 1.2.840.113556.1.4.1340
supportedControl   is 1.2.840.113556.1.4.1413
supportedControl   is 2.16.840.1.113730.3.4.9
supportedControl   is 2.16.840.1.113730.3.4.10
supportedControl   is 1.2.840.113556.1.4.1504
supportedControl   is 1.2.840.113556.1.4.1852
supportedControl   is 1.2.840.113556.1.4.802
supportedControl   is 1.2.840.113556.1.4.1907
supportedControl   is 1.2.840.113556.1.4.1948
supportedControl   is 1.2.840.113556.1.4.1974
supportedControl   is 1.2.840.113556.1.4.1341
supportedControl   is 1.2.840.113556.1.4.2026
isGlobalCatalogReady   is TRUE
forestFunctionality   is 2
supportedCapabilities   is 1.2.840.113556.1.4.800
supportedCapabilities   is 1.2.840.113556.1.4.1670
supportedCapabilities   is 1.2.840.113556.1.4.1791
supportedCapabilities   is 1.2.840.113556.1.4.1935
highestCommittedUSN   is 376377966
rootDomainNamingContext   is DC=myORG,DC=org
schemaNamingContext   is CN=Schema,CN=Configuration,DC=myORG,DC=org
namingContexts   is DC=myORG,DC=org
namingContexts   is CN=Configuration,DC=myORG,DC=org
namingContexts   is CN=Schema,CN=Configuration,DC=myORG,DC=org
configurationNamingContext   is CN=Configuration,DC=myORG,DC=org
serverName   is CN=myDomcontr01,CN=Servers,CN=myORG-West,CN=Sites,CN=Configuration,DC=myORG,DC=org


currentTime   is 20111123004547.0Z
domainFunctionality   is 2


RootDSE search completed.


SSL for encryption is enabled
SSL information:
    cipher strength: 128
    exchange strength: 1024
    protocol: Tls1Client
    hash strength: 160
    algorithm: Aes128
    KeyExAlgo: 41984


The certificate did NOT validate correctly
The cert information is:
  Subject: CN=myDomcontr01.myORG.org
 Issuer: CN=myORG USA Issuer CA 06 v1, DC=myORG, DC=org
 Expires: 8/21/2012 6:46:46 AM
 Hash: 6D8F0501B7881A0DCCC84E1DCF4E1DF0646A4479
 Public Key: 30818902818100C9D8ADE08D8CC893934C95AFF45DCFAB317B83CD0A93D659B181B8AB476D49954F94E2EE148C9A095C86592DCA458
B488DB3D5BDE5F14EAD3FBBB0D15A6DB1B48B587EB13984B15D27B2BEF4AF421BE8861B4A0C704A5510C5A2D431202675D65F9455573BDA2083D1DCD
6A2541FDA6CD6205FFACE670467366F9FC763B5C8B50203010001
 Serial: 1BC1C68D000000005EC9


Here's the c# code
https://s3.amazonaws.com/markgamache/doWork.cs

the .NET 2.0 assembly.
https://s3.amazonaws.com/markgamache/GetRootDSE.exe

Enjoy.

Monday, November 21, 2011

Learn From My Mistakes - Toddlers

I was recently reminded, twice, that kids don't see the world or understand language the way big people do. Here are two examples.

Be Careful
A few weeks ago, I was working out on our deck with a hammer. My 2 year old daughter came out and kept getting in the way. Being a wonderful and loving father, I warned my daughter. Using a tone that I knew was caring and not threatening, I said, "Sweetie, watch out or daddy might smash your toes with the hammer". My daughter immediately broke out into hysterical tears, screaming, "No daddy, don't smash my toes".  I guess one should think before they speak.

Dirty Apple
The other day my daughter was eating an apple out in the yard of a house we were looking at.  She was eating an apple, which she dropped into the dirt.   As the apple was covered in dirt, I told my daughter it was dirty and we'd get another one.  Then I threw it over the house into the green belt behind in the back.  Once again, my daughter broke out into tears, yelling, "daddy, apple disappear into sky"!!

Don't be like me...

Tuesday, May 24, 2011

Why We Use Hardware Security Modules

[Updated 5/22/2013] My statement, in the summary, about the limited value of an HSM when using soft keys was poorly articulated.

Hardware Security Modules (HSMs) are a security device that adds a lot of expense, man hours, and complexity to a data processing system. As security and usability are always a trade-off, let’s look at when you want to make the trade. First off, what do HSMs to at a basic level? An HSM is a device used for key management and encryption and decryption of data. The HSM holds the key material on the device and there is no way to export the keys in a usable format. This keeps and attacker from copying your encrypted database and then taking the key and decrypting the data offsite, on his own time, where he is less likely to be caught. Used correctly, this is a big security gain.
There are a few guiding principles to keep in mind when looking at the threats to your data and the protections that the proper use on an HSM can bring.
When considering how to implement key management, the other option we look at is software based keys. Let’s take a quick look at the trade-offs of each. As you will see, HSMs are not a silver bullet.
HSM
Software Keys
Someone with physical access to your server can take your keys*
Maybe
Yes
An attacker who can execute code on your servers can copy your keys
No
Yes
A rogue administrator can copy your keys
No
Yes
Use adds considerable extra expense
Yes
No
Use adds considerable complexity
Yes
No
Someone with root level access to your app server can see data before it is encrypted
Yes
Yes
*Properly configured, the keys are unusable even if the HSM is stolen.
While there are hundreds of specific threats and attack vectors against your data processing systems, it is important to align your controls to specific threats. In the case of using hardware encryption modules, there are three basics threats that might make us consider the use of an HSM over software based keys.
  1. The rogue administrator.
  2. Attackers with physical access to servers.
  3. Attackers who have root access on servers.
While there may be some other benefits offered by an HSM, they are ancillary and redundant to other controls that should be in place.
We need to understand a couple of basic HSM concepts before we can see what they do for us.
  • The Security World – This is a logical concept that can span more than one HSM. It is a group of HSMs that all share a common master key. Members of a security world can share application keys from other members in the world. Keys can be copied to security world members without possibility of comprise.
  • Smart Cards – The security world is run by and protected with smart cards. These cards are actually small computers that that can create keys, store them and perform operations using them. The cards can be protected with a PIN for additional security. The cards are designed to make it very difficult to copy a card in a short time and without destroying it.
  • k of n card sets – Many operations on an HSM require a high level of assurance, so the HSM can be setup to require more than one smartcard be used to perform an operation. The card set is sized and distributed so that it is unlikely that cardholders will be able to collaborate on subversive actions. The number of cards required to perform actions is called a quorum. A large n ensures that if cards are lost or destroyed enough can still be found to maintain uptime. k of n is based on Shamir’s Secret Sharing algorithm.
  • Administrator Card Set - The ACS cards run the security world, in conjunction with the HSM. ACS cards are used to backup and restore the security world. This includes adding new HSMs to the security world. The key that decrypts the backup file for disaster recovery and adding devices to the security world is base on the ACS and protected with the secret sharing algorithm.
  • Operator Cards – The OCS cards are used to access application keys. These are the keys that actually encrypt and decrypt the data. The OCS k of n can be different from the ACS k of n.
  • HSM Soft keys – The HSM soft keys these are application keys that can be used with no action from an OCS card set. All you need to do is boot the server holding the HSM, or the netHSM. If an attacker takes the HSM, they have unrestricted use of the key. They can’t export the key, but they can use the key at will to decrypt any stolen encrypted data.
When properly configured, the HSM keeps and attacker with privileged access or a rogue administrator from taking a copy of your encrypted data and copy of your key and decrypting your data at their leisure. The best the attacker can do is to grab data before it is encrypted or send encrypted data to the HSM for decryption. When looked at in conjunction with proper audit logs and some sort of IDS or IPS solution, this should significantly limit the time that the attacker has access to gather plaintext data.
If an attacker manages to steal an HSM they cannot copy your security worlds as they lack the ACS quorum. They cannot use OCS protected keys without the OCS quorum. HOWEVER, anything protected by HSM soft keys can be decrypted by simply putting the stolen HSM online in a new system.
The bottom line is this:
  • If you use an HSM with HSM Soft keys, you probably are wasting your money as you are not reducing risk when attackers have physical access. You can get the same logical access value with keys stored in the file system of the appropriate application tier. [Update] The HSM still provides lots of value, as a stolen HSM should go noticed.  You still do need to keep in mind that your operations, both physical and logical, may have a weak link that can lower the security of your overall system. 
  • If the attacker has root access at the right tier in your application, at a minimum, they can copy off the data before it is encrypted and worse case, they can call APIs to decrypt data at will.
HSMs are awesome, but don’t assume just they will solve your problems. In my experience, the biggest holes are created by the applications and APIs that rely on the HSMs.

Thursday, May 5, 2011

The Next Big Thing in Information Security

Many of us in the industry are bothered by the use of security vendors selling based on Fear, Uncertainty, and Doubt (FUD). FUD gets in the way of rational thought and often has a negative impact on proper prioritization and budgeting. Specific vulnerabilities may change, but the basics have not; Threats can come from the host, application, or network.

The latest “new” scary thing to fear is the Advanced Persistent Threat. This is terrifying!!! What is this new threat? The threat is just that virus and malware authors are getting better at their jobs. Now that there is a market for cyber-crime, hostage-ware and the like, the bad guys are getting more advanced. The free market is at work and the money attracts talent. All the APT does is makes itself really hard to remove. The bad guys are just finding more ways and have better logic behind their execution. In windows for example, they are placing the their code in many location, in multiple forms, running in multiple processes that reinforce each other, and that startup in many locations and for many reasons. Their code starts early and when you kill one of their processes, another re-instantiates it. They bad guys are just getting more thorough.

Now that the security marketing guys have invented this new scary threat, there is only one solution, my solution. We need to map a very specific control to a specific threat or vulnerability. There is only one control that can meet this threat head on; the “Advanced Persistent Control” or the “Advanced Persistent Control Suite”. These are really enterprise solutions. To address the consumer space; we need a product with “Advanced Persistent Protection”. No other compensating control maps so perfectly to the threat.

I have Googled, Binged, Yahooed, Patent and Trademark searched the heck out of these things* and get no hits, so I am in the process of filing the appropriate trademark, service mark, provisional patents and copyright paperwork to protect these names and technologies. Boy do I love how the patent office allows such insanely broad patents. I own these names, but will be willing to license them to security vendors if their products and bids qualify.

That’s right, Symantec, McAfee, Kaspersky, or an up and comer, line up and start bidding. For the right price, I will sell my rights completely; otherwise I may just license limited use of the names. I must warn you, don’t think you can just take these names. They are not in common use and they are mine. Like Michael “Let’s Get Ready to Rumble” Buffer, I plan to carefully and jealously guard my property.

Consumers beware, if you do not have Advance Persistent Protection, you are asking to be a victim of cyber-crime.

Corporations, without an Advanced Persistent Control Suite, you are not taking due diligence to protect your customers’ data and intellectual property. I smell grounds for gross negligence. Don't be a victim, like RSA.

Bidders, you can contact me at mark.gamache@gmail.com


*Ok, there was on unrelated hit on one of the terms. One!

Inputting falsified referrals to this site violates the terms of service of this site and is considered unauthorized access (hacking).